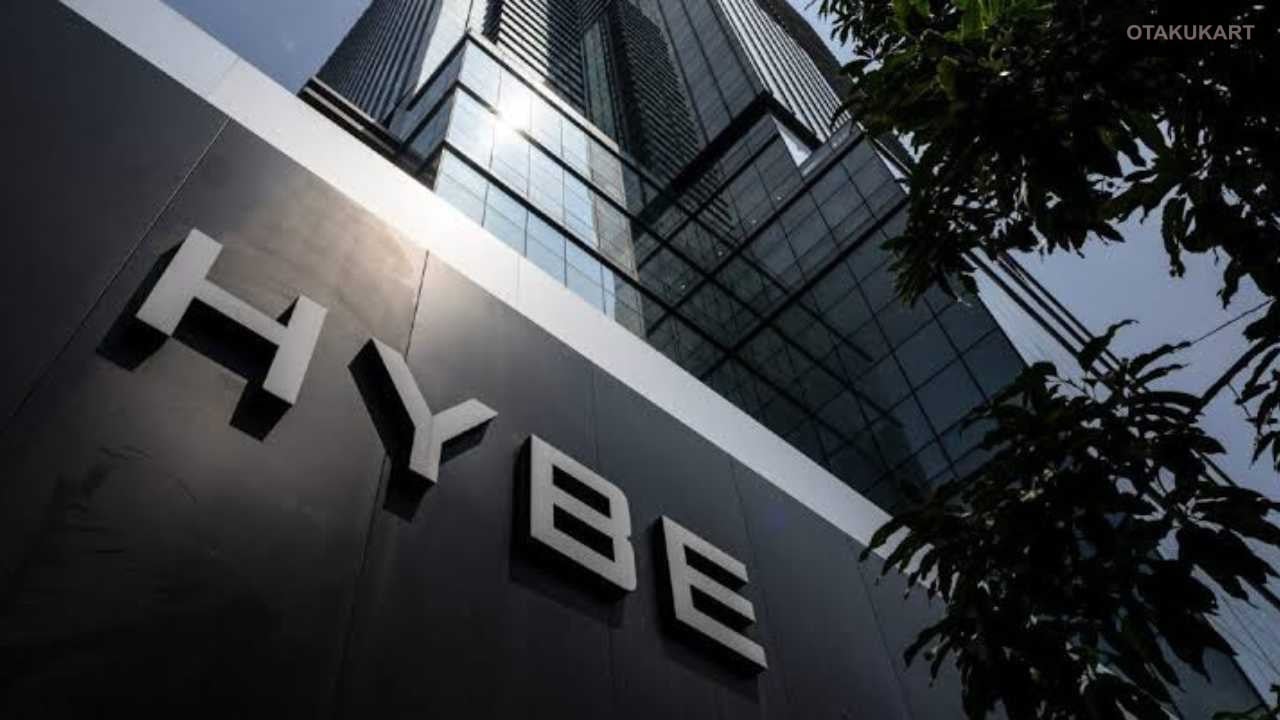
HYBE has issued an official apology following a data breach that exposed the personal information of its current and former employees, as well as individuals working for partner companies.
The incident involved unauthorized access to the company’s internal systems, raising concerns about the protection of sensitive employee information and the security measures used to safeguard corporate data.
On November 2, 2026, HYBE published a notice titled “Apology and Information Regarding the Personal Information Leak” on its official website, acknowledging that an internal security investigation had uncovered evidence of unauthorized access and information exposure.
According to the company, the compromised information included names, Korean resident registration numbers, passport numbers, bank account details, phone numbers, email addresses, and residential addresses.
Some personal information belonging to employees of partner companies was also affected.
The incident has brought attention to the importance of cybersecurity within major entertainment companies, particularly those managing extensive internal databases and sensitive employee records.
HYBE Reveals How Unauthorized Access Led to Employee Data Exposure
According to HYBE, the incident was discovered during an internal security inspection.
The company identified suspicious external access to a document-preview solution operated by an outside vendor and connected to its electronic approval system.
Further investigation revealed a similar vulnerability involving the company’s expense-processing system.
As a result, some internal documents and personal information stored across the two systems were accessed and leaked externally.
The unauthorized access reportedly occurred during two separate periods: September 12–13 and October 3–5, 2026.
The information potentially exposed varied between individuals.
In addition to names and contact details, the compromised records reportedly included resident registration numbers, foreigner registration numbers, passport information, bank and card numbers, medical information, dates of birth, employee identification numbers, department details, and automatically generated information such as IP addresses.
HYBE stated that it had taken immediate measures to prevent further exposure, including blocking the IP addresses and access routes used in the incident and suspending the affected document-preview service.
The company also confirmed that it had reported the incident to South Korea’s relevant authorities, including the Korea Internet and Security Agency (KISA) and the Personal Information Protection Commission.
In its official apology, HYBE stated:
“We sincerely apologize for causing concern due to the leakage of personal information.
We will work to prevent similar incidents from happening again by improving our security systems.”
The company also said that affected individuals would receive individual notifications explaining which categories of their personal information had been exposed.
HYBE Promises Stronger Security Measures Following the Incident
Alongside acknowledging the breach, HYBE addressed concerns about possible misuse of the exposed information.
The company stated that it had not received reports of suspected misuse at the time of its announcement.
However, it urged affected individuals to remain cautious about suspicious communications.
HYBE specifically warned against responding to emails, text messages, or messenger communications from people impersonating company departments or employees and requesting account information, money, or other sensitive details.
It also advised individuals not to open unexpected email attachments or click on links from unfamiliar sources.
The company further explained that individuals who experience losses because of the incident may seek compensation under South Korea’s Personal Information Protection Act.
They may also request dispute mediation through the Personal Information Dispute Mediation Committee.
HYBE reaffirmed its commitment to strengthening access controls and security monitoring across its internal systems.
It also promised to investigate the causes of the incident thoroughly and improve its security infrastructure to reduce the possibility of similar breaches in the future.
The incident comes amid wider attention surrounding data protection within HYBE and its affiliated businesses.
However, the company employee data breach should be distinguished from a separate information leak previously reported by its subsidiary Weverse Company.
With the investigation and individual notifications underway, HYBE’s immediate priority is addressing the exposure and strengthening its internal security measures.
The company has once again apologised to those affected and acknowledged the concern caused by the incident.